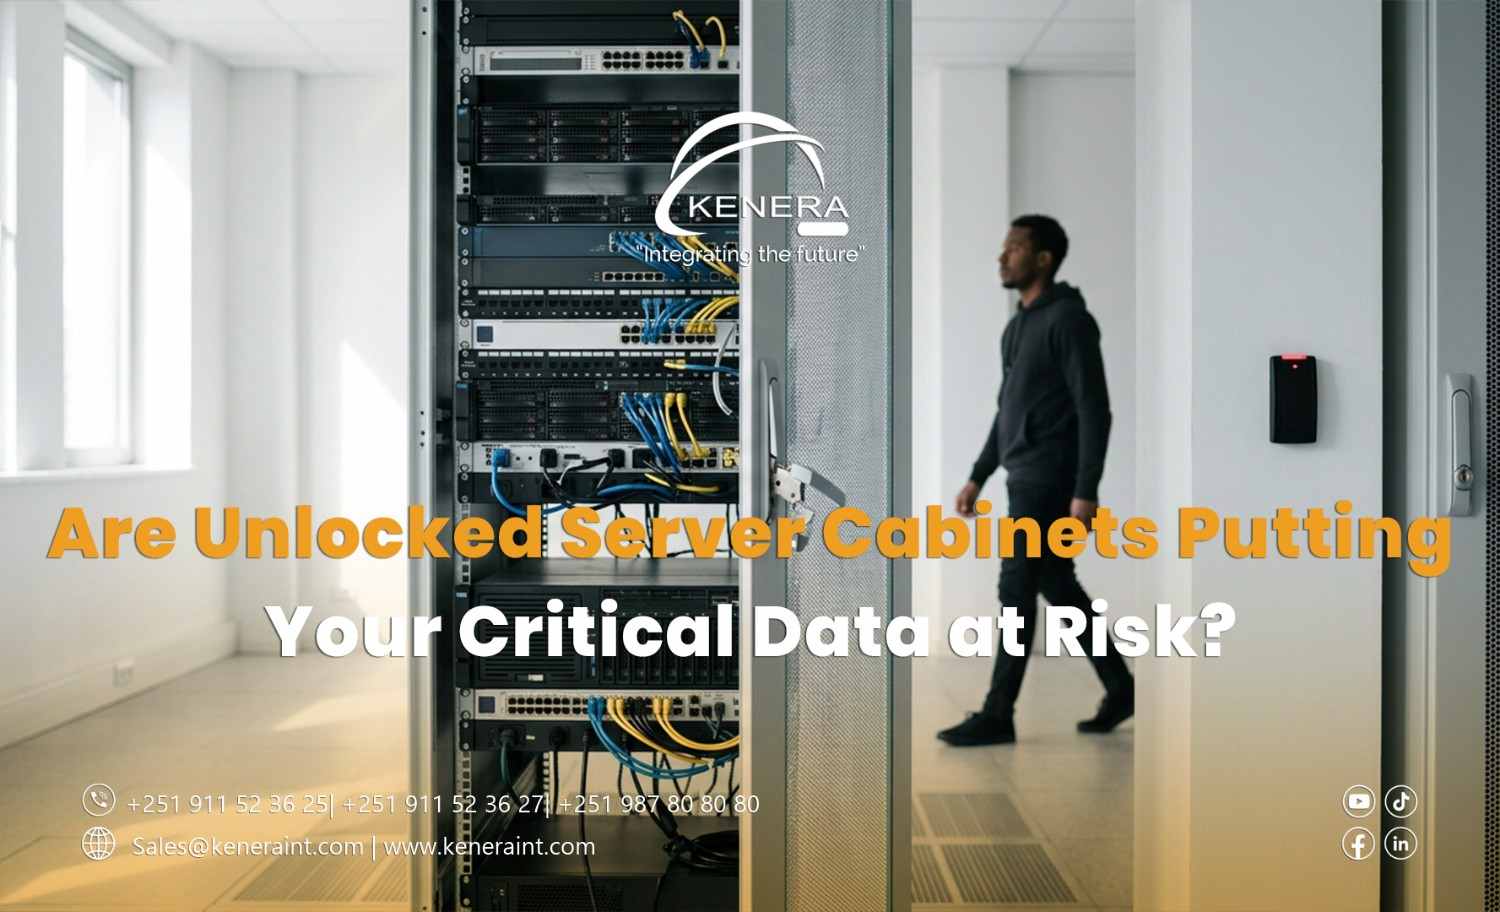
Are Unlocked Server Cabinets Putting Your Critical Data at Risk?
The company has invested in firewalls, endpoint protection, and network monitoring.
Every employee uses a password. Critical systems require authentication. The IT department regularly reviews cybersecurity alerts.
But inside the server room, a network cabinet stands unlocked.
A visitor, contractor, or unauthorized employee could potentially open it without triggering a single cybersecurity alert.
No password is required to touch a network cable.
No phishing email is needed to disconnect a server.
This is the overlooked side of enterprise cybersecurity: physical server security.
1. A Locked Server Room Is Not Always Enough
Many organizations assume their equipment is protected because the server room has a locked entrance.
However, technicians, cleaning personnel, maintenance contractors, and other authorized visitors may occasionally need access to that room.
Not everyone who enters should automatically have permission to handle every server, switch, storage system, or network connection.
Unlocked server cabinets remove an important additional layer of protection.
Cabinet locks help establish a second access boundary around critical infrastructure, particularly in shared facilities or environments where multiple teams use the same room.
2. What Could Someone Do With Physical Access?
Physical access creates risks that cybersecurity software alone cannot eliminate.
An unauthorized person could disconnect uplink cables, interrupt power connections, remove storage devices, or interfere with network equipment.
In certain circumstances, someone could connect an unauthorized device to an accessible network port or attempt to manipulate hardware.
The consequences may include service outages, equipment theft, unauthorized network access, or exposure of sensitive information.
However, opening a cabinet does not automatically provide access to encrypted data or authenticated systems. The actual risk depends on the equipment, its configuration, and existing security controls.
That distinction matters when evaluating server cabinet security risks.
3. The Insider Threat Is Not Always Intentional
Not every physical security incident involves malicious activity.
Imagine a contractor entering a server room to repair an air-conditioning component.
While moving equipment, the contractor accidentally pulls a cable connected to a production switch.
A critical application becomes unavailable.
Or consider an employee who opens a cabinet to investigate a blinking indicator and unintentionally disconnects the wrong device.
These situations illustrate why access control is also an operational reliability measure.
Limiting cabinet access reduces unnecessary interaction with sensitive infrastructure and helps ensure that authorized personnel perform maintenance.
4. Five Ways to Improve Server Cabinet Security
Organizations can strengthen physical infrastructure protection without redesigning their entire server room.
Install suitable cabinet locks. Use reliable mechanical or electronic locking systems appropriate for the cabinet design and operational environment.
Control key and credential distribution. Limit access to designated personnel, document who has permission, and promptly revoke access when responsibilities change.
Maintain access records. Where appropriate, use electronic access logs or documented key-control procedures to support accountability and incident investigations.
Protect exposed connections. Secure unused network ports, organize cabling, and prevent easy access to sensitive power and communication connections.
Inspect cabinets regularly. Check doors, hinges, locks, mounting hardware, and signs of tampering during routine infrastructure inspections.
Physical controls should complement—not replace—network segmentation, encryption, authentication, monitoring, and cybersecurity policies.
5. Consider Electronic Access Control for Critical Sites
For organizations operating multiple server rooms, data centers, or distributed branch infrastructure, traditional keys may become difficult to manage.
Electronic cabinet access systems can provide features such as individual credentials, centralized permissions, and access-event records, depending on the selected solution.
Some systems may integrate with broader physical security platforms.
These capabilities can improve accountability, but they also require proper administration, maintenance, emergency-access planning, and protection against unauthorized credential use.
The objective is controlled access, not unnecessary complexity.
Protect the Infrastructure Behind Your Digital Security
A strong cybersecurity strategy should account for both digital threats and physical vulnerabilities.
Firewalls protect network boundaries. Authentication helps control system access. Encryption protects information.
Physical security helps protect the equipment supporting all three.
Secure Your Critical ICT Infrastructure with Kenera International
Kenera International supports organizations in developing reliable enterprise ICT infrastructure, including secure network environments, structured cabling, and professionally planned server and network installations.
Because protecting critical business systems should not stop at the server room door.